Protect Your Business With DKIM and DMARC Email Security
At a glance
On this page
- 01 Quick answer – DKIM and DMARC Email Security
- 02 What to know first
- 03 Why it matters
- 04 Key decision areas
- 05 How to assess the right approach
- 06 What a review should cover
- 07 Business impact
- 08 Common pitfalls
- 09 Our delivery model
- 10 Interactive check
- 11 How Intellect IT can help
- 12 Frequently asked questions
QUICK ANSWER
The Practical Starting Point: What is DKIM and DMARC Email Security?
Business email remains one of the most trusted communication channels for invoices, approvals, customer updates and supplier instructions.
Whether it is a fake invoice, a targeted phishing link or an urgent payment request appearing to come from your CEO, these attacks often rely on one core trick: making a fraudulent email look like it came from a legitimate business.
That is why DKIM and DMARC email security are essential controls for organisations that rely on email. These DNS-based authentication controls help receiving mail systems verify that messages using your domain are authorised, making it much harder for attackers to impersonate your brand.
At Intellect IT, we look beyond basic spam filters. Email security is about protecting the operational trust your clients, staff and suppliers place in your name.
Key takeaways
DKIM proves authorised sending
DKIM adds a cryptographic signature to email sent by approved platforms. Receiving mail systems can check that signature against the public key published in your DNS records.
DMARC protects your visible domain
DMARC checks whether SPF or DKIM aligns with the visible “From” domain, then tells receiving systems whether to monitor, quarantine or reject messages that fail.
SPF, DKIM and DMARC work together
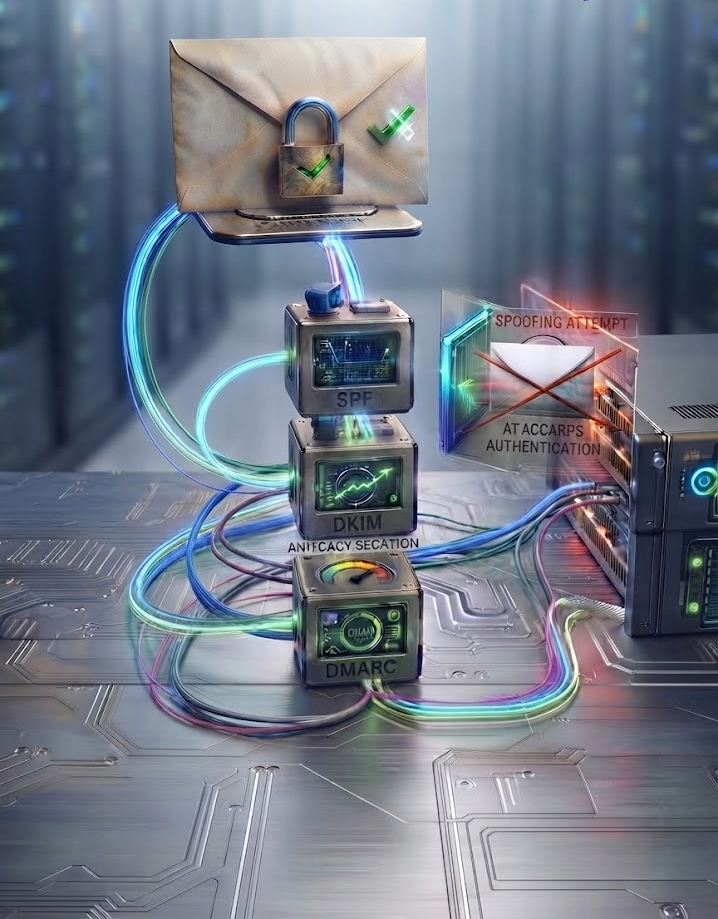
SPF identifies approved sending servers, DKIM validates a signed message, and DMARC applies alignment and enforcement rules to help reduce spoofing and business email compromise.
Start with monitoring
Use a DMARC policy of p=none first. This gives you visibility of systems sending email for your domain before you apply enforcement that could disrupt legitimate mail.
Review every email sender
Microsoft 365 or Google Workspace may not be your only senders. Check CRMs, marketing platforms, website forms, invoicing tools, support platforms and other third-party services.
Move to enforcement gradually
After legitimate senders are authenticated and aligned, progress from p=none to p=quarantine, then consider p=reject for stronger protection against unauthorised use of your domain.
Why DKIM and DMARC email security matters
Without correctly configured DKIM and DMARC records, it is easier for attackers to send email that appears to come from your business. An attacker may send a message that appears to come from [email protected] to request a fraudulent payment, steal credentials or deliver malware to a supplier, customer or staff member. For Australian organisations, email spoofing is not just a technical issue. It is a financial, operational and reputational risk.Why it matters
“Email authentication is about protecting the trust attached to your business name. If an attacker can convincingly impersonate your domain, they can exploit the confidence your clients, suppliers and staff have in your communications.”
Roy Solterbeck Intellect IT Director, Cybersecurity Expert
- Reduced impersonation risk: Makes it harder for criminals to use your exact domain in fake invoices, phishing messages and payment redirection scams.
- Better protection for clients and suppliers: Helps reduce the risk of external contacts receiving fraudulent messages that appear to come from your organisation.
- Improved email trust: Supports the legitimate delivery and credibility of business email sent through approved platforms.
- Visibility of email senders: DMARC reporting can reveal forgotten, misconfigured or unauthorised systems using your domain.
- Stronger Microsoft 365 security posture: Supports broader protection controls such as Microsoft Defender for Office 365, multi-factor authentication and staff awareness training.
Five DKIM and DMARC email security decision areas
A practical review of DKIM and DMARC email security should focus on five core decision areas:- Authorised sending platforms: Identify every system that sends email using your domain, including Microsoft 365, Google Workspace, CRM platforms, marketing tools, website forms, invoicing software and support systems.
- SPF record management: Confirm the SPF record accurately lists legitimate sending services without becoming overly complex, duplicated or exceeding DNS lookup limits.
- DKIM signing: Enable DKIM for Microsoft 365, Google Workspace and other supported third-party platforms, then confirm their signing domains align with your business domain where required.
- DMARC alignment and reporting: Publish a DMARC record, configure reporting addresses and review whether SPF or DKIM passes and aligns with the visible “From” domain. Microsoft’s DMARC configuration guidance for Microsoft 365 explains the DNS and alignment requirements for custom domains.
- Enforcement readiness: Progress from p=none to p=quarantine and eventually p=reject only after legitimate mail streams have been identified, configured and tested.
How to assess the right approach
The right approach to DKIM and DMARC email security starts with visibility. Before applying strict enforcement, your organisation needs to understand which platforms send email using its domain and whether each sender is properly authenticated.-
Step 01Identify every platform sending email for your domain
-
Step 02Review and correct the SPF record
-
Step 03Enable DKIM signing for approved services
-
Step 04Publish DMARC in monitoring mode
-
Step 05Review reports and move towards enforcement
- Identify every sender: Document all systems using your domain in an email address or visible “From” field. Include staff email, CRMs, marketing platforms, website forms, invoicing tools, ticketing systems, HR software and any managed services.
- Review the SPF record: Confirm legitimate sending platforms are authorised. Remove obsolete services where appropriate and avoid adding providers without confirming they genuinely send email for your domain.
- Enable DKIM: Publish the required DNS records and turn on DKIM signing in Microsoft 365, Google Workspace or the relevant third-party platform.
- Start DMARC at p=none: Publish a DMARC record that collects aggregate reporting without requesting quarantine or rejection of failed mail.
- Fix alignment issues: Review reports, identify legitimate services that fail, then correct their SPF, DKIM or visible “From” domain configuration before increasing enforcement.
- Progress carefully: Move to p=quarantine when legitimate senders are consistently passing, then consider p=reject when the domain is ready for full enforcement.
What an email authentication review should cover
A review of DKIM and DMARC email security should examine the DNS records, email platforms and practical sending behaviour that determine whether your domain can be protected without disrupting legitimate business communications.- Domain inventory: Identify primary domains, subdomains, parked domains and any domains used for business email, marketing campaigns or transactional communications.
- SPF configuration: Review current SPF syntax, authorised services, DNS lookup count, duplicate records and obsolete sending platforms.
- DKIM configuration: Confirm DKIM is enabled for Microsoft 365, Google Workspace and each supported third-party sender, with required public DNS keys correctly published.
- DMARC policy: Review the existing policy, reporting addresses, alignment settings, percentage enforcement and whether p=none, p=quarantine or p=reject is appropriate.
- Visible From addresses: Check whether the domains used in visible “From” addresses align with SPF-authenticated domains or DKIM signing domains.
- Third-party platforms: Review CRM, accounting, marketing, website, support, HR and other service providers that may send email on behalf of your business.
- Website and application email: Confirm website forms, WordPress notifications, transactional email services and application alerts send from authorised and properly authenticated sources.
- DMARC reporting: Review aggregate reports for unknown senders, failed authentication, alignment issues, unexpected activity and services that need correction.
- Enforcement plan: Establish a documented path from monitoring to quarantine and reject, with clear approval points before tighter policies are applied.
The goal is not simply to publish three DNS records. The goal is to ensure that legitimate business mail remains reliable while unauthorised use of your domain becomes substantially harder.
Business impact: from impersonation risk to control
DKIM and DMARC work quietly in the background, but the impact extends beyond DNS. Proper email authentication helps protect the trust your organisation has built with customers, suppliers, staff and business partners. A well-managed DKIM and DMARC email security programme can deliver:- Reduced payment-fraud exposure: Makes it more difficult for criminals to impersonate your organisation in fake invoice, bank-detail change or urgent payment-request scams.
- Protection for customers and suppliers: Helps reduce the likelihood that people outside your business receive fraudulent messages appearing to come from your domain.
- Improved sender trust: Supports the reputation and deliverability of legitimate business email sent through approved systems.
- Better visibility: DMARC reporting can identify forgotten business platforms, misconfigured software and unauthorised attempts to use your domain.
- More controlled technology decisions: Provides a clear process for approving new platforms that need to send email on behalf of the business.
- Stronger security posture: Complements Microsoft Defender for Office 365, multi-factor authentication, secure email gateways, endpoint protection and staff awareness training.
Consider the alternative. Without effective authentication, a fraudulent message can carry your business name, appear to come from a familiar address and reach a client or supplier before they have any reason to suspect it is fake.
Email authentication will not stop phishing from lookalike domains or prevent attacks from compromised accounts. It does, however, close a preventable gap by making it much harder for attackers to send unauthorised messages using your genuine domain.Common DKIM and DMARC email security pitfalls
The most common mistake is treating DMARC as a single DNS record rather than an ongoing email-authentication process. A record can be published, but it will not deliver meaningful protection if legitimate senders remain unknown, DKIM is incomplete or enforcement is applied too early.- Moving straight to p=reject: Strong enforcement is the end goal for many organisations, but applying it before legitimate senders are identified can block invoices, CRM emails, website enquiries and important operational notifications.
- Leaving p=none indefinitely: Monitoring is valuable, but it is not enforcement. If p=none remains in place permanently, receiving systems are not being asked to quarantine or reject unauthorised messages.
- Forgetting third-party senders: CRM, marketing, accounting, support and website platforms are often missed because they do not sit within the main Microsoft 365 or Google Workspace environment.
- Publishing multiple SPF records: A domain must have one valid SPF record. Multiple records can produce a permanent error and cause legitimate mail to fail SPF checks.
- Exceeding SPF lookup limits: Complex SPF records can exceed the permitted DNS lookup limit, causing SPF evaluation to fail. Consolidate and manage sending services carefully.
- Not enabling DKIM: DMARC can pass with aligned SPF or DKIM, but relying on SPF alone can create avoidable gaps. Enable DKIM where supported for better resilience across sending environments.
- Ignoring alignment: A sender can technically pass SPF or DKIM but fail DMARC if the authenticated domain does not align with the visible “From” domain.
- Not reviewing reports: DMARC aggregate reports can reveal unknown senders, authentication failures and configuration problems. They need regular review and follow-up.
- Assuming email authentication stops all phishing: DKIM and DMARC help protect your genuine domain. They do not stop lookalike domains, compromised accounts or every social-engineering attack.
How email authentication works
How SPF, DKIM and DMARC help protect your domain
Receiving email systems assess authorised sending sources and signed messages, then use DMARC alignment and policy settings to decide how to handle mail that claims to come from your business domain.
Email source
Authorised sender
Signed message
Alignment and policy
Inbox decision
How Intellect IT can help
At Intellect IT, we help Melbourne businesses and professional home-office users create a secure home Wi-Fi network with stronger router security, sensible device separation and reliable access for the technology that matters.
Whether you need to protect a home office, separate smart devices or improve business connectivity, we can help you put the right network foundations in place.
How Intellect IT helps protect your business domain with DKIM and DMARC
Phase 1 – Understand your email environment
- Identify business domains: We review the domains and subdomains used for staff email, transactional email, marketing, website communications and customer-facing services.
- Map authorised senders: We identify platforms that may send email using your domain, including Microsoft 365, Google Workspace, CRM systems, marketing tools, invoicing platforms, website forms, support systems and managed applications.
- Understand business-critical mail: We clarify which email flows are operationally important, such as invoices, customer notifications, website enquiries, service alerts, marketing campaigns and supplier communications.
Phase 2 – Review SPF, DKIM and DMARC configuration
- Assess SPF records: We review whether the SPF record accurately authorises legitimate email platforms, avoids duplicate records and remains within DNS lookup limits.
- Review DKIM signing: We confirm whether DKIM is enabled for supported platforms and whether the required public keys and CNAME records are correctly published in DNS.
- Check DMARC alignment: We assess the DMARC policy, visible “From” domains, alignment results, reporting addresses and whether the current configuration is suitable for monitoring or stronger enforcement.
Phase 3 – Configure monitoring and resolve failures
- Establish reporting visibility: We configure or review DMARC aggregate reporting so your organisation can see which platforms are sending email for the domain and whether they pass authentication.
- Investigate legitimate failures: We identify authorised services that fail SPF, DKIM or alignment checks and provide practical recommendations to correct their configuration.
- Identify unknown activity: We help distinguish expected sending services from obsolete, misconfigured or potentially unauthorised use of the domain.
Phase 4 – Progress to stronger domain protection
- Apply a staged policy: We help establish a safe path from p=none monitoring to p=quarantine and, where suitable, p=reject enforcement.
- Protect legitimate communications: Before enforcement is increased, we confirm that approved mail streams such as Microsoft 365, CRM, invoicing, website and marketing systems are correctly authenticated.
- Reduce spoofing opportunity: Stronger DMARC policy settings make it more difficult for attackers to use your exact business domain in impersonation and fraud attempts.
Phase 5 – Maintain email authentication as your business changes
- Review new platforms: We help assess new marketing, CRM, invoicing, website and business systems before they begin sending email on behalf of your domain.
- Maintain sender visibility: Regular review helps identify changes to email platforms, failures in existing configuration and unexpected activity that needs investigation.
- Support broader email security: DKIM, SPF and DMARC work alongside Microsoft Defender for Office 365, multi-factor authentication, endpoint security and staff awareness training as part of a stronger security posture.
The goal is not simply to publish DNS records. It is to make legitimate business email reliable, give your organisation visibility of every sender using its domain and make unauthorised impersonation substantially harder.
Interactive check
DKIM and DMARC Email Security Check
Answer four quick questions to identify whether your business domain has sensible email authentication foundations or whether SPF, DKIM, DMARC or third-party sender settings may need attention.
Do you know every platform that sends email using your business domain, including Microsoft 365, CRM, marketing, invoicing, website and support systems?
Is your SPF record valid and does it accurately authorise the platforms that legitimately send email for your domain?
Is DKIM enabled for Microsoft 365, Google Workspace and other supported platforms that send email using your domain?
Do you have a DMARC record, review its reporting and have a planned path from monitoring to stronger enforcement?
Your email authentication position
Answer all four questions to see your directional result.
This is a quick directional check, not a detailed DNS, Microsoft 365, email security or DMARC implementation assessment.
Decision support
What does your current email authentication position look like?
Select the description closest to your current position.
Fast answers
Common DKIM and DMARC email security questions
Tap a question for a short, practical answer.
What is the difference between SPF, DKIM and DMARC?
Does DMARC require both SPF and DKIM to pass?
Should we move straight to a p=reject DMARC policy?
Do DKIM and DMARC stop every phishing email?
Ready to protect your email domain?
Intellect IT can review your SPF, DKIM and DMARC email security configuration, identify legitimate email senders and help you progress towards stronger protection without disrupting business email.
Talk to our Melbourne team about an email-authentication review.
QUESTIONS, ANSWERED
Frequently asked questions
FAQs – DKIM and DMARC email security
What is the difference between SPF, DKIM and DMARC?
Does DMARC require both SPF and DKIM to pass?
What does a DMARC policy of p=none mean?
Should my business move straight to p=quarantine or p=reject?
Are DKIM and DMARC included with Microsoft 365?
Can website forms, CRMs and invoicing tools cause DMARC failures?
Yes. These platforms can send legitimate email using your domain but fail DMARC if their SPF or DKIM configuration does not align with the visible “From” address. This is why all third-party sending platforms should be identified and reviewed before stronger DMARC enforcement is enabled.

Ready when you are
Ready to experience
IT that just works?
Talk to an IntellectIT specialist. No obligation, no sales pitch, just honest advice for your business.